Case Study / DevOps & Platform · SaaS
Automated SaaS releases with built-in security checks
A GitHub Actions pipeline builds, scans, tests, and deploys SaaS applications to AWS EKS, replacing manual releases with automated quality gates and notifications at every stage.
- Domain
- DevOps & Platform Engineering
- Workload
- SaaS application delivery
- Runtime
- Kubernetes on AWS EKS
- Provisioning
- Terraform · Infrastructure as Code
Measured impact
Manual steps from commit to production
Automated stages — build, scan, deploy, release
Security gates on every release (SonarQube + Trivy)
Parallel unit, E2E & UI testing on each candidate
Terraform-provisioned, drift-free EKS environments
Real-time Slack visibility across the pipeline
01 / Overview
The operating context.
In modern software development, speed without quality is a liability — and quality without speed is a competitive disadvantage. Most engineering teams face the same painful reality: manual deployments are slow, error-prone, and inconsistent.
Security vulnerabilities slip through undetected, testing is rushed under delivery pressure, and by the time a bug reaches production the cost of fixing it has multiplied many times over.
02 / Challenge
What stood in the way.
Three critical problems demanded an intelligent solution:
- 01
Manual deployment processes were slowing release cycles and creating inconsistent, unreliable delivery.
- 02
Security and code-quality checks were disconnected from the delivery workflow — catching problems too late.
- 03
Teams lacked real-time visibility into the pipeline — blind spots created risk and reduced confidence.
03 / Solution
What Algorims built
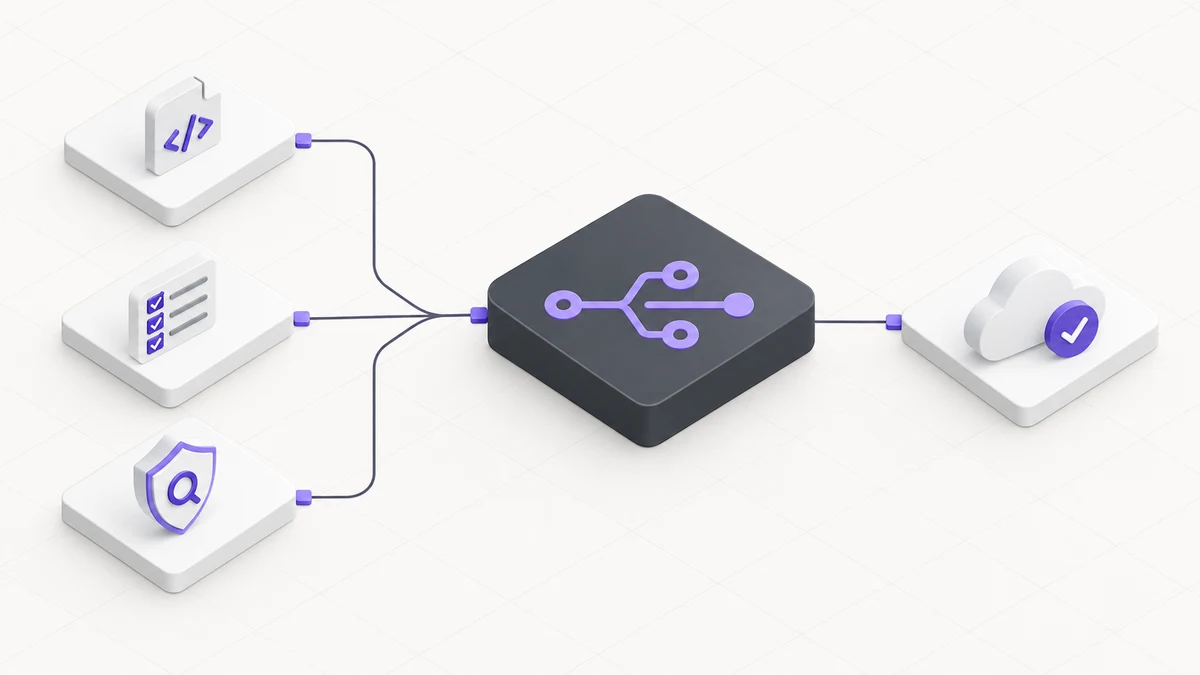
RaaS — Release Automation as a Service — a fully automated, security-first CI/CD pipeline that takes code from commit to production with zero manual intervention, engineered across four precision-designed stages.
Stage 1 — Code & build
The moment a developer commits, the pipeline activates automatically. Source code is compiled, validated, and built into an optimised container image — ready for the next stage within minutes, not hours.
Stage 2 — Scan & package
SonarQube performs deep static analysis and Trivy scans for vulnerabilities across the image and dependencies. Only clean, secure, quality-verified code advances — eliminating the risk of security debt reaching production.
Stage 3 — Deploy & test
The verified app deploys to a dedicated AWS EKS staging environment provisioned automatically via Terraform. Unit, end-to-end, and UI tests run in parallel, delivering fast, reliable feedback before anything reaches production.
Stage 4 — Notify & release
Stakeholders receive real-time Slack notifications at every stage. Once all gates clear, the verified release ships to production seamlessly, automatically, and with full confidence.
System stack
Production foundations.
- GitHub Actions
- Docker
- SonarQube
- Trivy
- Kubernetes
- AWS EKS
- Terraform
- Slack
04 / Results
What changed after delivery.
Deployment speed dramatically increased — commit to production in a fraction of the time, zero manual intervention.
Security built into every release — automated SonarQube and Trivy scans ensure only vulnerability-free code ships.
Quality assured at every stage — unit, end-to-end, and UI tests run automatically on every candidate.
Infrastructure as code — Terraform-provisioned EKS environments are consistent, repeatable, and cost-effective.
Complete pipeline visibility — real-time Slack notifications keep every stakeholder informed.
Engineering teams unblocked — developers focus on features, not deployments.